Commodity derivatives position limits adopt revised breach penalties, broad commodity criteria, and client open-position limits based on deliverable s...
IT Resilience Index requires market infrastructure institutions to automate resilience scoring, early warnings, and continuous service-delivery monito...
Urgent interim relief exception permits commercial suit without pre-institution mediation where immediate disclosure and asset protection are genuinel...
ODR arbitration participation remains mandatory after failed conciliation, while jurisdictional and maintainability objections stay available before t...
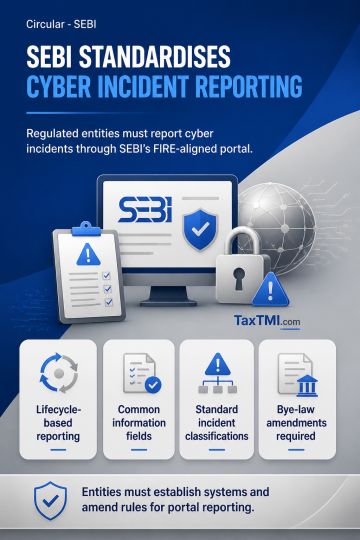
Cyber incident reporting by regulated entities must be made through SEBI's Cyber Incident Reporting Portal, aligned with the Financial Stability Board's Format for Incident Reporting Exchange (FIRE). The aligned portal requires structured reporting using common information fields, standard definitions and consistent incident classifications, supporting harmonised reporting. It permits reporting across the incident lifecycle, including initial notification, intermediate updates and final closure, recognising that complete information may not be available initially. Regulated entities must establish systems to implement the portal-based reporting requirement and make any necessary amendments to their bye-laws, rules or regulations. The requirement operates alongside applicable cybersecurity and cyber-resilience reporting obligations.
Cyber incident reporting by regulated entities must be made through SEBI's Cyber Incident Reporting Portal, aligned with the Financial Stability Board's Format for Incident Reporting Exchange (FIRE). The aligned portal requires structured reporting using common information fields, standard definitions and consistent incident classifications, supporting harmonised reporting. It permits reporting across the incident lifecycle, including initial notification, intermediate updates and final closure, recognising that complete information may not be available initially. Regulated entities must establish systems to implement the portal-based reporting requirement and make any necessary amendments to their bye-laws, rules or regulations. The requirement operates alongside applicable cybersecurity and cyber-resilience reporting obligations.
Note: It is a system-generated summary and is for quick reference only.
 TaxTMI
 TaxTMI